Agentic AI Architecture: Core Components Explained
Learn how agentic AI architecture works, from context and reasoning to planning, orchestration, tools, memory, agents, and human oversight.
11 min readby Prithvi
AI agents are often described as if they are simply language models with access to tools.
That explanation is useful, but incomplete.
A language model can understand a request and generate a response. An agentic system has to do considerably more. It needs to understand a goal, gather the right context, decide what to do next, interact with external systems, evaluate what happened, and continue until the task is complete—or stop and ask for help when it reaches a boundary.
That makes agentic AI less about a single model and more about the architecture surrounding the model.
A useful way to think about an agentic system is:
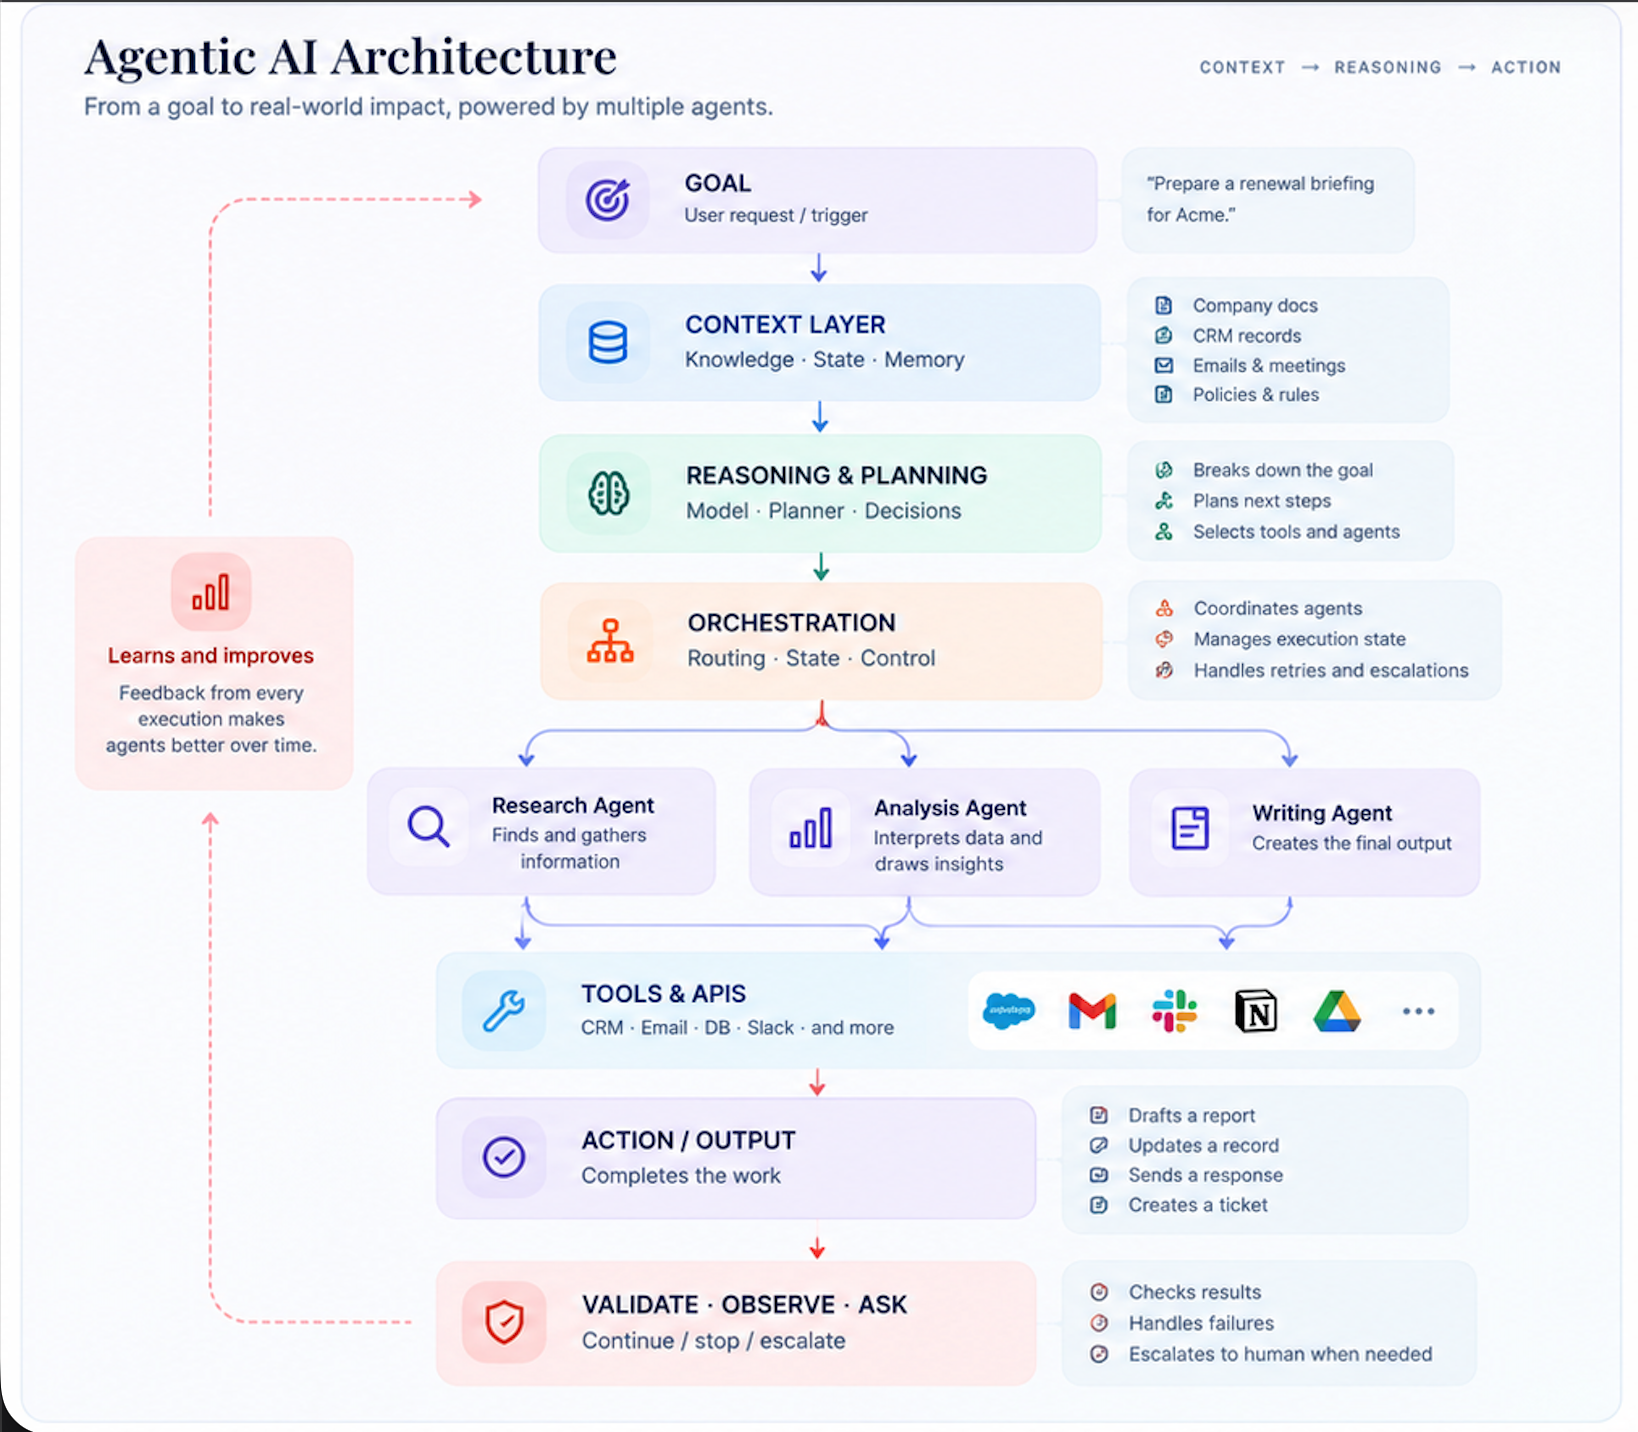
Goal → Context → Reasoning → Planning → Orchestration → Agents → Tools → Action → Validation
Each layer has a different job. Together, they turn an AI model from something that produces answers into a system that can actually perform work.
What is agentic AI architecture?
Agentic AI architecture is the collection of components that allows an AI system to pursue a goal across multiple steps.
At the simplest level, a traditional AI application might look like this:
Prompt → Model → Response
An agentic application introduces a much longer loop:
Goal → Context → Plan → Act → Observe → Evaluate → Act again
That difference is important.
Imagine asking an AI system to prepare renewal briefings for every enterprise customer whose contract expires in the next 90 days.
The system first needs to identify the relevant accounts. It then needs to retrieve information about those customers, understand their recent interactions, determine what information belongs in a renewal briefing, and generate the briefings. If a CRM request fails halfway through, it needs to recover rather than starting the entire process again.
And if generating the briefing is fine but sending it externally requires approval, the system needs to know when to stop and ask a human.
That is an architecture problem.
*The architecture of an agentic AI system
A production agentic system typically contains several interconnected layers.
The architecture doesn't necessarily need every component to be a separate service. In a simple application, several of these responsibilities may live inside one agent.
As systems become more complex, however, separating these responsibilities makes them easier to control, observe, and scale.
1. The goal: what is the system trying to accomplish?
Every agentic system begins with a goal.
That goal might come from a person, a scheduled process, an event in another system, or another application.
The difference between a useful agent and a glorified chatbot often starts here.
“Summarize this document” has a relatively fixed outcome. There isn't much need for the system to determine what should happen next.
“Find our highest-risk enterprise accounts and prepare renewal briefings” is different. The system has to decide what information it needs, where to find it, how to interpret it, and what constitutes a completed task.
A well-designed agent therefore needs more than an instruction. It needs a definition of the desired outcome and the boundaries within which it can operate.
That gives the rest of the architecture something to work toward.
2. Context: giving the agent the right information
An agent can only reason about the information available to it.
This makes context one of the most important parts of agentic architecture.
For an enterprise agent, context might come from company documents, CRM records, emails, meetings, support tickets, databases, internal policies, previous decisions, or the user's own work.
The challenge isn't simply connecting the agent to every available source.
The challenge is determining which context matters for the task at hand.
Consider a sales agent preparing for a customer meeting. It might have access to thousands of company documents, but the useful context could be limited to the customer's CRM record, recent emails, previous meeting notes, open support issues, and the latest contract.
Good agentic architecture therefore treats context as a dynamic layer rather than a giant information dump.
The agent retrieves what it needs, reasons over that information, and carries the relevant state forward as the task progresses.
3. Memory and state: remembering what has already happened
Context tells an agent what it needs to know. State tells it what has already happened.
This becomes critical when a task spans multiple steps.
Imagine an agent processing 18 customer accounts:
Task started
↓
Found 18 relevant accounts
↓
Reviewed 12
↓
Tool failed on account 13
↓
Retry
↓
Continue from account 13
Without state, the system may lose its place and start again from the beginning.
With state, the orchestrator knows that twelve accounts have already been processed, which tool failed, what information was retrieved, and where execution should resume.
Memory can also persist across tasks, allowing systems to retain useful information over time. But persistent memory introduces its own questions around permissions, accuracy, retention, and governance.
The important distinction is that memory isn't just storage. It is part of the system's ability to maintain continuity while pursuing a goal.
4. Reasoning and planning
The model sits at the center of the reasoning layer.
It interprets the goal, determines what information is relevant, considers possible actions, and decides what should happen next.
But reasoning and planning shouldn't be confused with execution.
Suppose an agent receives the instruction: Prepare a renewal briefing for Exa.
The model might determine that it needs to retrieve the customer's CRM record, review recent meetings, inspect open support issues, and look at the current contract.
That is the plan.
Actually retrieving those records requires tools. Deciding which systems can be accessed requires permissions. Coordinating those operations requires orchestration.
This distinction matters because it prevents the common mistake of thinking that the language model itself is the entire agent.
The model provides intelligence. The surrounding architecture turns that intelligence into reliable execution.
5. Orchestration: coordinating the system
Once an agentic system contains multiple steps, tools, or specialized agents, something needs to coordinate them.
That is the role of orchestration.
The orchestrator manages the flow of execution. It can determine which agent should handle a task, which tool should be called, what context should be passed forward, what state needs to be preserved, and what should happen if an operation fails.
For example, a research-heavy task might look like this:
User request
↓
Research Agent
↓
Analysis Agent
↓
Product Agent
↓
Writing Agent
↓
Human review
The individual agents have different responsibilities, but the orchestrator gives the overall workflow structure.
This becomes particularly important when systems need to recover from failures, run tasks in parallel, hand work between agents, or stop for human approval.
Orchestration is therefore the control layer between individual capabilities and the larger workflow.
6. Agents: specialized reasoning and execution
An agent is responsible for pursuing a particular goal or part of a larger workflow.
Simple applications may use one agent. More complex systems can divide work across specialized agents.
A research agent might gather information. An analysis agent might interpret that information. A product agent might turn the analysis into a recommendation, while a writing agent creates the final document.
This specialization can make complicated workflows easier to reason about.
But adding agents isn't automatically better.
Every additional agent introduces another handoff, another source of state, and another place where something can go wrong. The right architecture uses multiple agents when specialization genuinely improves the workflow—not simply because “multi-agent” sounds more sophisticated.
This is also where autonomous agents become relevant.
An autonomous agent is able to operate through multiple steps toward an objective rather than waiting for a human to specify every individual action.
7. Tools and APIs: giving agents the ability to act
Reasoning alone doesn't complete a business process.
Agents need tools.
A tool might allow an agent to search a knowledge base, retrieve a CRM record, query a database, create a ticket, update a document, send an email, or schedule a meeting.
This is the point where AI moves from generating information to interacting with the systems where work actually happens.
But tools also create boundaries.
Reading a customer record is different from modifying it. Drafting an email is different from sending it. Querying a database is different from changing production data.
Agentic architecture therefore needs to define not just what tools are available, but also what each tool is allowed to do.
Permissions, approval requirements, input validation, and failure handling become part of the architecture.
8. The execution loop
These components come together in an execution loop.
The agent receives a goal and retrieves the context it needs. It reasons about the task and creates a plan. The orchestrator determines how that plan should be executed, invoking agents and tools as required.
The system then observes what happened.
If the result is incomplete, it can continue. If a tool fails, it can retry or choose another path. If the task requires human judgment, it can pause and ask.
That creates a loop rather than a single request-response interaction:
Understand → Retrieve → Plan → Act → Observe → Evaluate → Continue or stop
This is one of the defining characteristics of agentic systems.
The system isn't simply generating the next token. It is using the outcome of one step to determine what should happen next.
9. Validation, observability, and recovery
An agent that can take action also needs to know whether its actions worked.
This is where validation and observability become important.
Consider the earlier example of processing 18 accounts. If the CRM request fails on account 13, a production system shouldn't simply return an incomplete result without explanation.
It should be able to identify the failure, determine whether the operation can be retried, preserve the state of the previous twelve accounts, and continue from the point of failure.
That might look like:
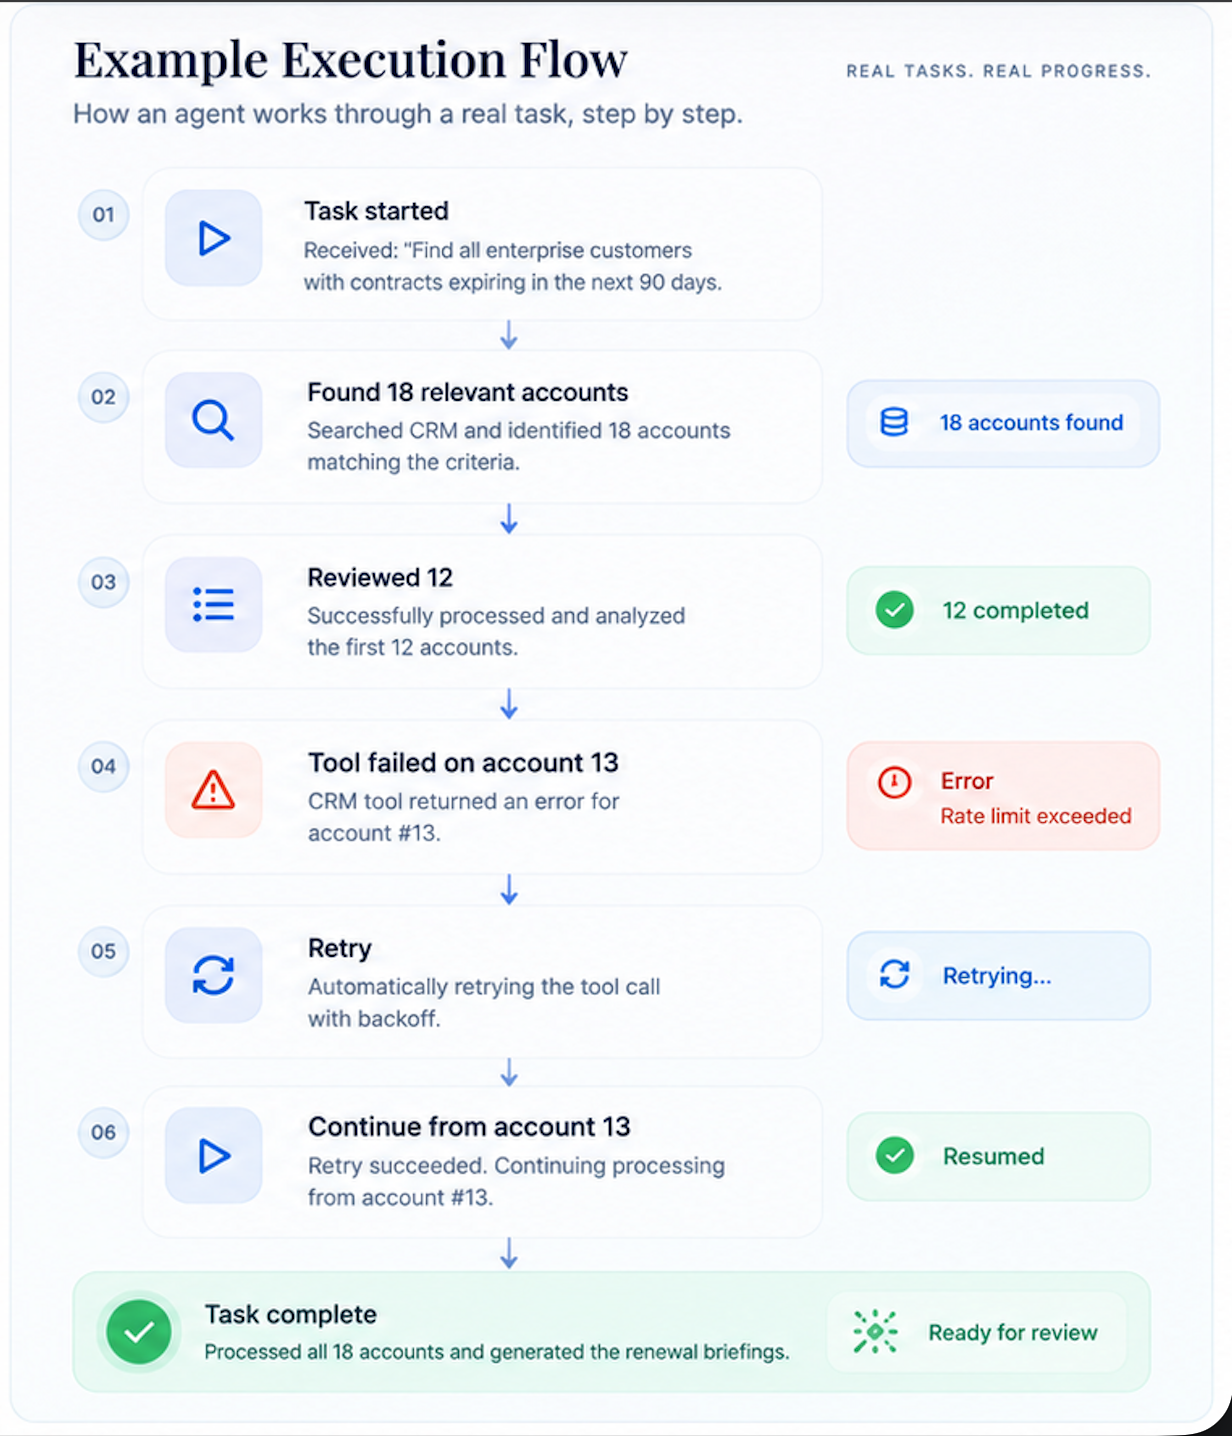
The execution trace is valuable for more than recovery.
It lets teams understand what an agent actually did, which sources it used, which tools it called, where it encountered uncertainty, and why a particular action was taken.
For enterprise AI, that visibility is essential.
10. Human oversight and governed execution
Autonomous doesn't have to mean unsupervised.
In a production environment, the most useful agentic systems are often designed around graduated autonomy.
An agent might be free to search documents, analyze records, summarize information, or prepare a draft. But when the workflow reaches a consequential action—such as sending an external communication, changing a customer record, approving a transaction, or making a contractual commitment—the system can stop and request approval.
This creates a much more practical model of autonomy:
Assist → Draft → Act with approval → Act within defined boundaries
The goal isn't to maximize the number of decisions an agent makes independently.
The goal is to let the system handle the work that can safely be automated while preserving human judgment where it matters.
Putting the architecture together
A mature agentic AI system can therefore be understood as a set of layers working together:
The goal defines what needs to happen.
The context layer gives the system the information required to reason about the task.
Memory and state maintain continuity throughout execution.
The model provides reasoning and planning.
Agents provide specialized capabilities.
Orchestration coordinates those capabilities.
Tools and APIs connect the system to the outside world.
Validation and observability make execution measurable and recoverable.
Governance determines what the system is allowed to do and when a human needs to intervene.
The resulting architecture looks less like a chatbot and more like an operating system for AI-driven work.
Agentic AI architecture vs. traditional AI
The difference is easiest to understand by looking at how the systems behave.
| Traditional AI | Agentic AI |
|---|---|
| Prompt → response | Goal → execution |
| Generates an answer | Pursues an outcome |
| Usually single-step | Multi-step |
| Limited external action | Uses tools and APIs |
| Little or no persistent state | Maintains state and memory |
| Fixed interaction | Can adapt based on results |
| Human performs the next action | System can perform the next action |
| Output-focused | Outcome-focused |
The important distinction isn't that agentic systems are always fully autonomous.
It's that they are designed around completing goals rather than simply producing responses.
Where Libra fits
This architecture is particularly important in enterprise environments because company work rarely exists in one place.
The information required to complete a task might be spread across documents, meetings, email, CRM records, project systems, databases, and internal knowledge.
An agent can have access to all of those systems and still perform poorly if it doesn't have the right context at the right time.
That's where Libra WorkBase fits.
WorkBase provides the context and execution layer around enterprise AI: connecting company knowledge and business systems, reasoning across that context, and allowing workflows and agents to take governed actions.
The architecture can therefore be thought of as:
Company context → reasoning → orchestration → agents → tools → governed execution
Instead of asking employees to gather context manually and move information between systems, the WorkBase approach gives AI a connected environment in which it can understand the work and help move it forward.
When should you use agentic architecture?
Agentic architecture is most valuable when a task has a meaningful outcome but isn't completely deterministic.
A support workflow is a good example.
A ticket arrives. The system needs to understand the issue, find relevant company knowledge, look at the customer's history, determine a likely resolution, draft a response, and escalate when the situation falls outside its rules.
A sales workflow can work similarly. The system might identify a quiet opportunity, inspect the account's recent activity, understand what happened in previous conversations, and prepare a contextual follow-up.
In both cases, the system has to interpret information and adapt its next step. A traditional rule-based automation can handle parts of the process, but the agentic layer becomes useful when the workflow requires reasoning.
Not every automation needs an agent.
If a process is completely deterministic, conventional automation may be simpler and more reliable.
Agentic architecture becomes valuable when the system needs to understand, reason, adapt, and act.
The future of agentic AI architecture
The next generation of enterprise AI is unlikely to be one giant autonomous agent responsible for everything.
Instead, we'll see systems composed of specialized capabilities operating over shared context and coordinated through orchestration.
A research capability can find information. An analytical capability can interpret it. A domain-specific agent can make a recommendation. Another agent can turn the result into an output. A human can approve the consequential step.
What makes this useful isn't any individual agent.
It's the architecture connecting them.
That is ultimately the shift happening with agentic AI.
The question is moving from: “What can this model answer?”
To: “What work can this system understand, coordinate, and complete?”
And answering that question requires much more than a language model. It requires the architecture around it.